Topic
Banking App Permissions: What Users Grant, Risks That Follow
A mobile banking app needs far less access than most users assume. The gap between what is requested and what is needed is where privacy risk lives.
A mobile banking app needs far less access than most users assume. The gap between what is requested and what is needed is where privacy risk lives.
A plain-English map of the software categories a working law firm depends on, from practice management to e-discovery, and where each one fits in the workflow.
Regulatory examinations follow a rhythm of routine, targeted, and follow-up reviews. Learn what examiners request and how fintech firms can prepare all year round.
How to size and structure a compliance team for a supervised firm: obligation mapping, common models, skills and records, and warning signs of a strained team.
Grant Thornton's four-part model treats DSA compliance as an operating capability, not a one-time build.
After New Year's Day, sourcing specialty metals, tungsten or rare earths from China, Russia, North Korea or Iran requires an accepted mitigation plan — and the clock is under 100 days.
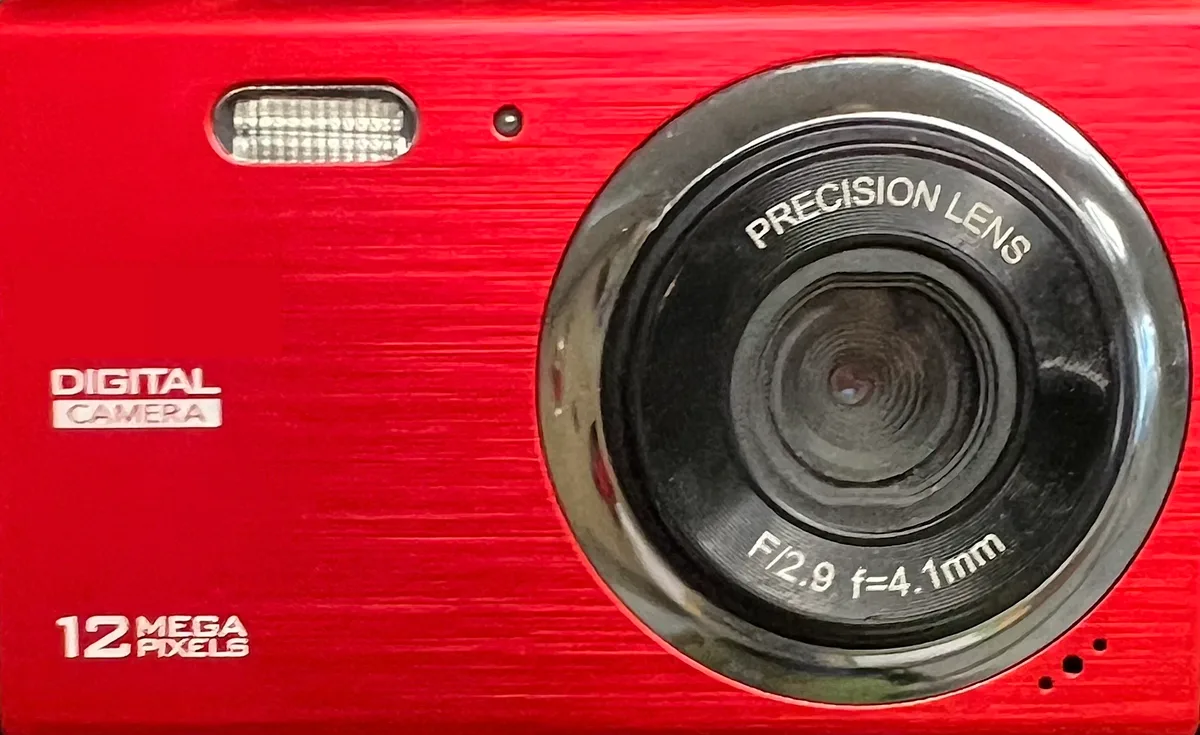
Sensor size, real zoom, and battery discipline explain the niches where a dedicated camera still beats the phone in your pocket.
A practical checklist for compliance-minded readers who want to know what an app asks for, who stands behind it, and what it admits to collecting.
The federal rule behind EFT error resolution, and what it actually obliges a bank or fintech to do when a transfer goes wrong.
A practical explainer for compliance and legal-ops teams on how no-code platforms convert shared spreadsheets into governed mobile and web apps.